LLMjacking: How a Leaked AI Key Can Turn Into a Surprise Cloud Bill
If your team uses ChatGPT-style tools, AI APIs or AI coding assistants, there is a new risk you can measure in dollars.
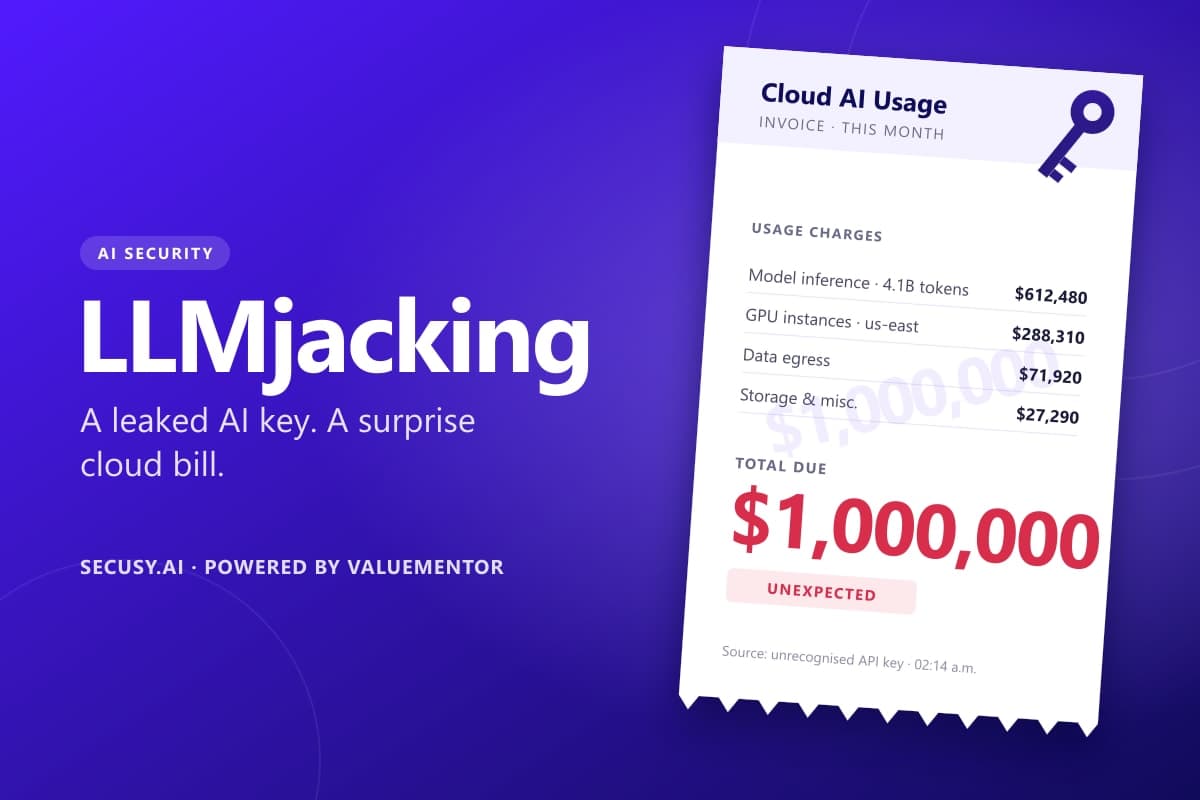
Google reports that stolen AI access, called "LLMjacking", is costing some companies up to $1 million in cloud bills. Attackers steal an AI or cloud key, then run expensive AI workloads on your account. You find out when the invoice arrives.
Small businesses are not too small to target. Attackers scan for leaked keys automatically. They do not care whose account it is.
Two risks, in plain language
1. Leaked AI keys. An API key is a password for software. If one ends up in a code repository, a shared document or a developer's laptop that gets compromised, anyone can use it. Every request they make is billed to you.
2. Forgotten AI tool connectors (MCP servers). AI coding assistants can install small "connector" programs, called MCP servers, so they can reach your files, databases and apps. They are often installed automatically, never tracked and never updated. An outdated connector is an open door to your code, your secrets and your keys.
A 5-step check you can do this week
- List your AI services. Write down every AI tool and cloud AI service your business pays for, and who owns each one.
- Find your keys. Ask your developers where AI and cloud keys are stored. Keys belong in a secrets manager, not in code, spreadsheets or chat messages.
- Rotate old keys. Any key older than 90 days, or shared between people, should be replaced.
- Set a spending alarm. Turn on budget alerts and usage limits in your cloud and AI provider consoles. A spike at 2 a.m. should wake someone up, not wait for month-end.
- Ask about connectors. Ask your team which AI coding tools they use and what connectors those tools have installed. Remove anything nobody can explain.
Why this matters for compliance too
Customers and auditors are starting to ask how you govern AI. ISO/IEC 42001 is the standard for managing AI responsibly, and ISO/IEC 27001 already expects you to control secrets, suppliers and changes. Getting your AI keys and tools in order now puts you ahead of those questions.
How Secusy helps
Secusy gives small businesses a fixed-scope, affordable way to get this right:
- Cloud and AI configuration review — we find exposed keys, risky permissions, missing spend alerts and unmanaged AI connectors.
- AI governance starter pack — policies and controls aligned to ISO/IEC 42001 and ISO/IEC 27001, sized for an SMB.
- Clear report — prioritised fixes and an estimate of your cost exposure, in plain English.
Delivered by ValueMentor, a CREST-accredited cybersecurity firm.
Not sure where your AI keys are? That is the first thing we will find.
Sources
- The Rise of LLMjacking: How Threat Actors Monetize Compromised Cloud and Model Resources — Google Cloud Blog
- LLMjacking: AI Model Hijacking Reaches Black Market Scale — Cloud Security Alliance research note